Know what’s in
your software.
Know what to do next.
From component inventories to enterprise decisions. Practical guidance for understanding, operating and buying SBOM technology.
Primary sources. Practical tests. Buyer-side requirements.
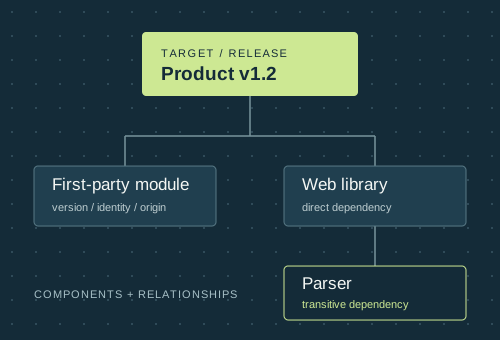
An SBOM describes components and relationships.
Your workflow turns that data into decisions.
2026 minimum-elements guidance · FDA February 2026 · CRA reporting now applicable
Sources reviewed Oct 4, 2026 ↗An inventory is the beginning.
A Software Bill of Materials is a machine-readable inventory of software components, versions, identities and relationships. It helps producers and consumers investigate what is in a defined release.
It supports vulnerability response, supplier risk, component governance and procurement. It needs validation, release mapping, fresh intelligence and accountable action to become useful.
Understand the artifact and its limits →Understand
Concepts, standards and requirements
02Operate
Generate, validate, consume and monitor
03Select
Evaluate capability with your own evidence
04Procure
Compare costs and protect the buyer
Ask the questions that matter.
Choose a useful inventory.
Build a repeatable operating model.
Can your tools exchange it?
SPDX and CycloneDX are common exchange formats. Exact versions, fields and relationship preservation matter more than a format logo.
Compare formats →Which obligation applies?
FDA submissions, EU products, federal acquisitions and customer contracts have different scopes. Separate legal duties from guidance.
Check requirements →What happens after generation?
Validate the inventory, map it to releases, investigate vulnerability applicability and assign response. Schema validity is one check.
Plan validation →Make the demonstration
answer your questions.
Test transitive coverage. Ingest a supplier file. Investigate ambiguity. Export everything. Agree on acceptance before implementation.
Use the software selection guide →Follow the work, end to end.
Technical guides and practical buyer tools.
All resources are ungated.
Understand
Concepts · requirements · referenceWhat is an SBOM?
A Software Bill of Materials (SBOM) is a machine-readable inventory of software components, their identities and their relationships within a defined product or artifact.
Government guidanceSBOM minimum elements: the current baseline
The July 2026 CISA and partner guidance updates and replaces NTIA’s 2021 minimum-elements report.
Standards comparisonSPDX vs CycloneDX: formats, versions and interoperability
Choose an SBOM format by the information you need to exchange and the versions your producers and consumers actually support.
Practical guideSBOM vs VEX: composition and vulnerability applicability
An SBOM describes software composition.
Requirements hubSBOM requirements: identify the authority and the scope
There is no single global SBOM requirement.
Statute + final guidanceFDA SBOM requirements for medical devices
Section 524B(b)(3) of the FD&C Act requires an SBOM for commercial, open-source and off-the-shelf components in covered cyber-device submissions.
EU regulation · phased applicationCyber Resilience Act SBOM requirements
The EU Cyber Resilience Act requires in-scope manufacturers to draw up an SBOM as part of vulnerability handling.
Current federal policySBOMs in U.S. federal software procurement
Current OMB policy uses agency-defined, risk-based software and hardware assurance.
ReferenceSBOM FAQ
Direct answers to common technical, requirements and software-buying questions, with links to the evidence and practical guides..
ReferenceSBOM glossary
Use these definitions to keep inventory, analysis, standards and procurement discussions precise.
Primary-source librarySources and standards library
Primary sources for the site’s requirements and technical claims.
Editorial policyAbout SBOM Software and our editorial methodology
SBOM Software is a reference site for understanding inventories, operating SBOM workflows and purchasing supporting technology.
Operate
Generation · quality · lifecycleHow to generate an SBOM that describes what ships
Generate an SBOM at a defined lifecycle point, bind it to an exact artifact and release, and validate the coverage.
Practical guideSBOM generators and tools: evaluate by evidence
An SBOM generator discovers or assembles component information and emits an inventory.
Practical guideHow to validate an SBOM: syntax, identity and coverage
Validation has two separate jobs: determine whether the document follows its declared format, and determine whether its content accurately describes the intended software.
Practical guideSBOM management: from files to an operational inventory
SBOM management links component inventories to products, releases, suppliers, deployments and accountable owners.
Practical guideUse an SBOM for vulnerability management
An SBOM becomes useful for vulnerability response when component identity, advisory intelligence, applicability analysis and remediation workflow are connected to product releases and deployed assets..
Practical guideSBOMs for healthcare organizations: the buyer’s workflow
A healthcare organization consumes inventories to understand purchased software and devices, investigate component exposure and coordinate supplier response.
Practical checklistSBOM readiness checklist
Readiness means you can produce or receive a useful inventory, associate it with a release, investigate a component question and act through an accountable workflow.
Select
Capabilities · evidence · evaluationSBOM vs SCA: do you need additional software?
An SBOM is a software-composition data artifact.
Buyer recommendationSBOM software: capabilities and buying decisions
SBOM software can generate, ingest, validate, normalize, retain and exchange inventories, then connect them to vulnerability and lifecycle workflows.
Buyer recommendationHow to select SBOM software: an enterprise buyer’s guide
Start with use cases, evidence and acceptance criteria.
Procure
Pricing · requirements · agreementsSBOM software pricing: normalize the meters and the scope
Compare quotes using identical usage assumptions and complete meter definitions.
Buyer recommendationSBOM software RFP requirements and buyer protections
A useful SBOM RFP asks for implemented capability, exact versions, limitations, evidence, delivery effort, responsibility, price and an acceptance test.
No matching guide. Try a broader term or clear the search.